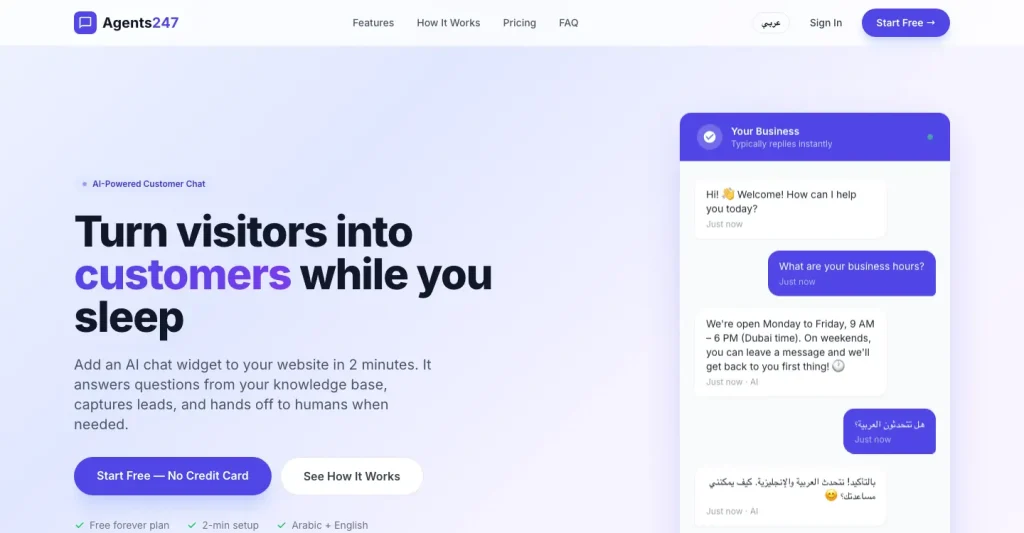
Agents247
AI customer support · SaaS
An embeddable AI chat widget that answers from a knowledge base, captures leads and hands off to humans. One script tag, Arabic and English.
Visit agents247.app (opens in a new tab)Service
Built with Lovable, Replit, Bolt.new, v0, Base44, Emergent, Google AI Studio or Cursor? Get a production readiness review before real users and payments.
A bounded repair has a different scope from a full build, assessment or takeover.
A working preview is a starting point. Before launch, you need to know who can access each record, how payments are verified, where secrets live and how you will detect and recover from failures. Our AI-built app production check turns those questions into a written, prioritized review.
Lovable app production readiness review: we inspect the available code, sign-in flows, database access rules, uploads and payment handling. If your app uses Supabase, its row-level security policies are part of the agreed backend review.
Replit app code review and launch checks: we examine the application and available deployment configuration, environment secrets, data persistence, error reporting and behavior after a restart.
Bolt.new app audit: we trace generated frontend and backend flows, check where authorization runs and review the database, payment integration and deployment setup you actually use.
v0 by Vercel prototype-to-production review: we distinguish working product flows from placeholder screens, then inspect available server routes, authorization, data handling, configuration and error states.
Base44 app production readiness assessment: we agree which application settings, permissions, integrations and user journeys can be inspected. Managed platform internals or unavailable source code are recorded as review limitations.
Emergent app launch review: we examine the accessible generated application, API authorization, secrets, database boundaries, payment flows and deployment configuration.
Google AI Studio app review: we inspect the available application code, API key handling, client and server boundaries, AI usage costs and deployment setup. The checks depend on whether the project is a web or mobile app.
Cursor-built app code review: we review the resulting codebase, dependencies, tests, access controls and release process. The checks follow your application's stack and hosting rather than assuming Cursor supplies a particular backend.
You receive findings with evidence, a prioritized fix list and a walkthrough. A code review or production readiness assessment is not a penetration test, security certification or guarantee that an app has no defects. Fixes, deployment work and app rescue are agreed separately after the review. CodeFounders is independent of the platform vendors.
Start with the guide for your app builder or coding tool.
How it works
We agree the repository, backend and hosting access available, test accounts and a suitable test environment. Do not send passwords or API keys in the enquiry form.
We check sign-in, data access, secrets, payment flows, deployment and agreed load scenarios within that scope.
Findings ranked by launch risk, evidence, fix estimates and anything we could not verify.
Ready within the reviewed scope, ready after fixes, or rebuild, with the next steps explained.
Related work
AI customer support · SaaS
An embeddable AI chat widget that answers from a knowledge base, captures leads and hands off to humans. One script tag, Arabic and English.
Visit agents247.app (opens in a new tab)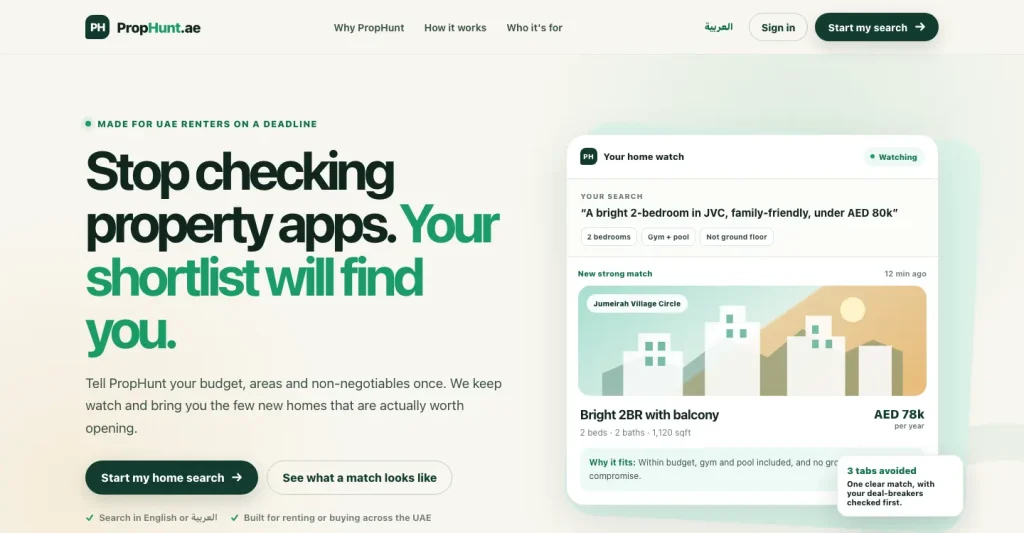
PropTech · AI · Mobile
Renters describe the home once, in English or Arabic. New matches arrive by WhatsApp and email, each with a plain-language reason.
Visit prophunt.ae (opens in a new tab)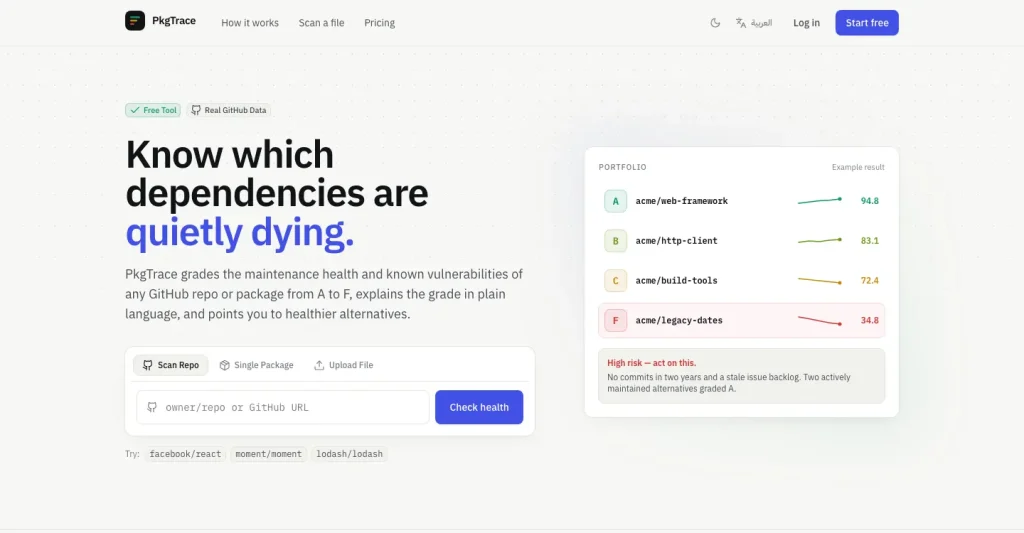
Developer security
Grades the maintenance health of open-source dependencies from A to F, with team portfolios, bulk scans, webhooks and API tokens for CI.
Visit pkgtrace.com (opens in a new tab)Questions
We scope reviews for apps built with Lovable, Replit, Bolt.new, v0 by Vercel, Base44, Emergent, Google AI Studio and Cursor, as well as Claude Code and hand-written code. We confirm the code, backend and deployment access needed before accepting a review.
The production check identifies launch blockers and recommends what to fix, finish or rebuild. Implementation is a separate agreed scope; the review does not include repairs or promise that every app can be kept.
We can assess accessible settings, permissions, integrations and user flows if that scope is useful. We state what cannot be verified and do not describe a limited-access assessment as a full code audit.
Not during the check. We agree a suitable test environment and review access first. Any production testing or later code changes require separate agreement.
No. It is a production readiness review of the agreed application scope, with findings and limitations. Specialist penetration testing or compliance assessment is a separate service to arrange where needed.
We explain the evidence, what can be retained and the estimated work so you can decide whether to repair or rebuild.
In 20 minutes you will know whether this is the right next step, roughly what it takes, and the biggest risk to watch.